DNS over HTTPS: What It Protects and What It Doesn't
Understand DNS over HTTPS, resolver privacy, DNS over TLS and Android Private DNS. Learn what encrypted DNS changes and what remains visible.
Kayla
Quetta Networks


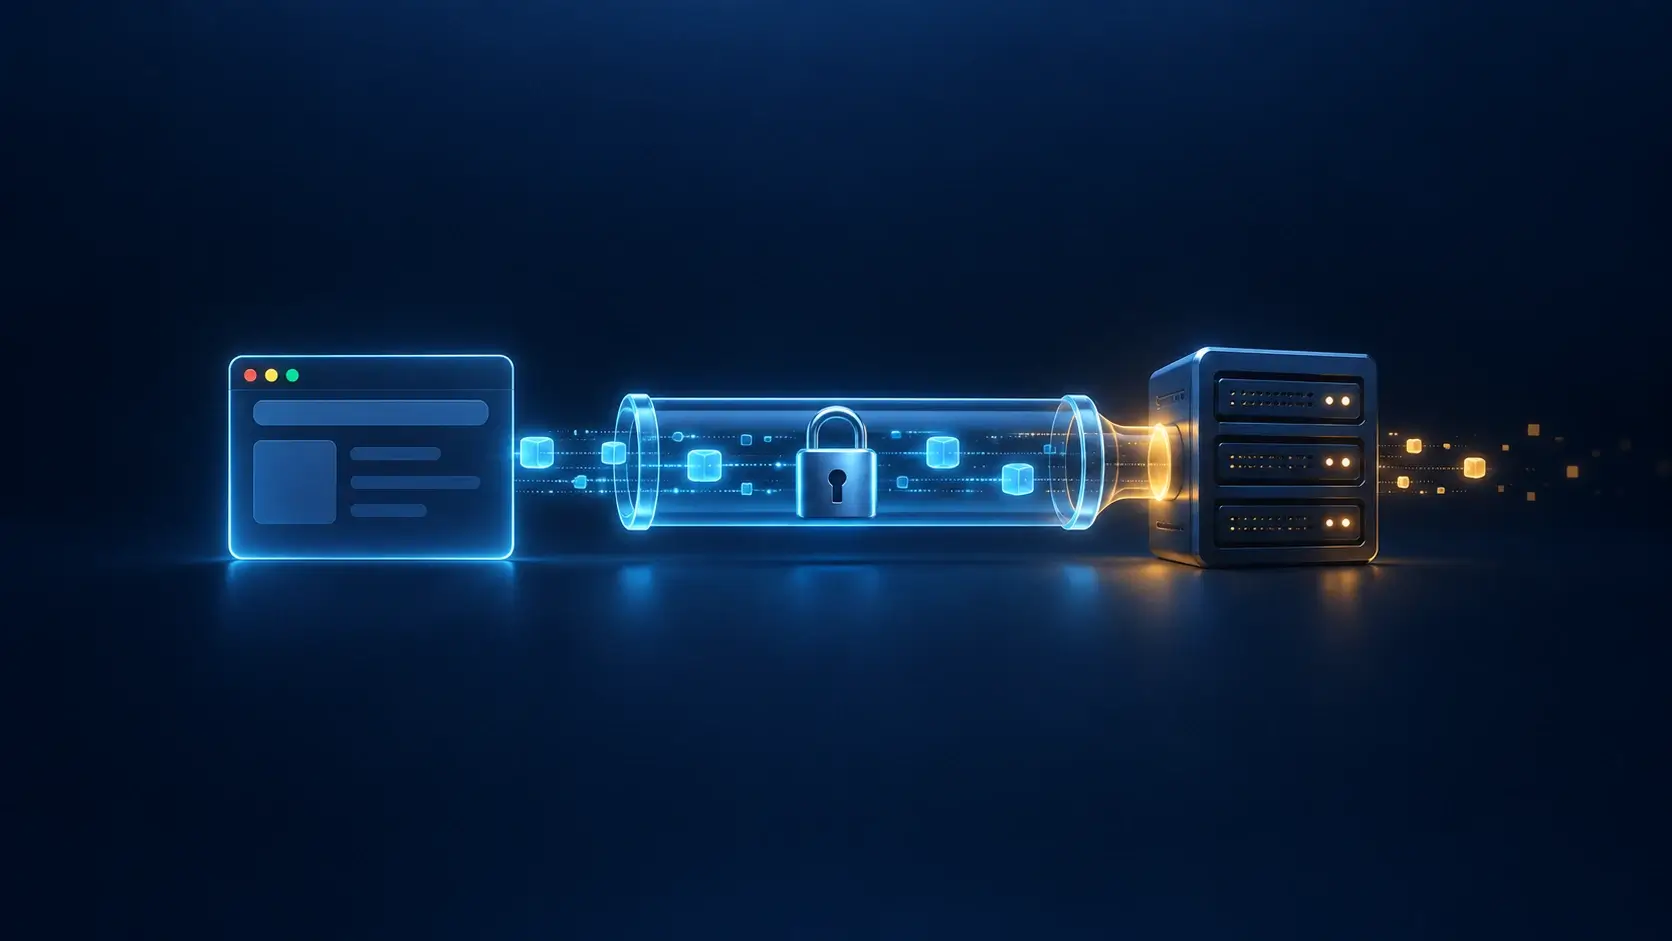
DNS over HTTPS, or DoH, sends DNS questions and answers through an encrypted HTTPS connection. It protects that exchange between a client and its chosen resolver from direct reading or alteration along the connection. It does not make browsing anonymous, hide a signed-in identity, or automatically block ads.
The protocol is defined in IETF RFC 8484. To understand its value, separate three choices: who answers your DNS questions, how those questions travel, and whether the answers are filtered.
What is a DNS resolver?
A DNS resolver helps turn a name such as example.com into information a device can use to reach a service. Your device may use a resolver supplied through the network, while a browser or app may have its own DNS configuration.
The resolver is an intermediary you trust with those questions. Encrypting the connection to it changes who can observe the exchange in transit; it does not remove the intermediary from the process.
What does DNS over HTTPS protect?
DoH protects the DNS exchange carried over its encrypted connection. Someone monitoring that network path cannot simply read those questions as ordinary plaintext DNS traffic. This is useful, for example, when you want a protected connection to a resolver you have deliberately chosen.
That protection has a specific scope. A DoH setting in one browser does not prove that another app uses encrypted DNS, nor that every connection on the device follows the same route. Cloudflare's DoH documentation
Question | What enabling DoH means |
|---|---|
Are these DNS queries encrypted in transit to the resolver? | Yes, when they actually use the configured DoH connection |
Does the resolver become unable to see the queries? | No; ordinary DoH still involves trusting the resolver |
Does the website lose access to my signed-in account? | No |
Are advertisements automatically filtered? | No; filtering is a separate resolver policy or tool |
Is every app on the device covered? | Not established by a browser setting alone |
Cloudflare distinguishes ordinary DoH from approaches designed to separate a client's identity from its DNS questions. That distinction is a useful reminder that encryption and anonymity solve different problems. Oblivious DNS over HTTPS
DNS over HTTPS vs DNS over TLS
DoH and DNS over TLS, or DoT, both protect DNS transport with encryption. DoH carries the exchange using HTTPS. DoT uses a dedicated TLS connection for DNS, commonly on port 853. Neither name tells you whether the chosen provider filters advertisements or how long it retains data. Cloudflare's DoT documentation
Term | Describes | Does not establish |
|---|---|---|
DoH | A DNS transport over HTTPS | The provider's logging or filtering policy |
DoT | A DNS transport over TLS | Complete device coverage or anonymity |
Private DNS | An Android setting for DNS privacy/configuration | That every browser and app uses an identical path |
Filtering DNS | A resolver policy that blocks selected domains | Whether the transport is encrypted |
Android's Private DNS settings are not simply another name for a browser's DoH switch. Use the provider's instructions for the specific setting and Android version. Google's help explains the Private DNS control and its DNS-only scope. Android network settings
Is public DNS better than ISP DNS?
“Public” and “ISP-provided” describe the service relationship, not a privacy rating. The useful questions are whether the provider supports the transport you need, what it records, how it handles failures, whether it applies filtering and whether it is suitable for your network.
Before changing providers, read the current policy and setup documentation. A custom resolver can give you a different policy or filtering choice. It is not a universal speed upgrade, and it may not resolve names that exist only inside a workplace or school network.
For a personal device, make the change for a specific reason you can check. “I want domain filtering from this provider” is a clearer goal than “custom DNS must be more private.”
Does encrypted DNS block ads?
Encryption protects transport. Ad filtering is a separate function. A resolver can provide encrypted DNS without blocking advertising domains; a filtering resolver can combine domain rules with an encrypted connection.
If you specifically want DNS-based filtering on Android, follow the AdGuard DNS setup guide. For the difference between domain rules and page-level filtering, read how ad blockers work.
Why can browser DNS and device DNS behave differently?
A browser configured to use a particular resolver may send its DNS questions along a different path from applications using the device's default network settings. A VPN can also change routing or DNS handling.
When checking a setup, write down the active browser DNS setting, device DNS setting and VPN state. Test one change at a time. A provider's diagnostic result can help identify the resolver used for that test; it does not prove that every app follows the same path.
If a site stopped opening after a change, restore the previous setting and compare. Do not confuse changing a provider with flushing a DNS cache, which addresses a different layer.
Where encrypted DNS fits in browser privacy
Even with encrypted DNS, a website can recognize an account you sign in to and process information you submit. Cookie controls, tracker blocking, permissions and account choices still matter.
Use the browser privacy guide to map those remaining risks to the appropriate controls. It also explains when browser protections are useful and when a separate network decision is required.
Frequently asked questions
Is DoH the same as a VPN?
No. DoH protects DNS exchanges on its configured connection. A VPN changes the routing of traffic within its coverage. Neither description alone tells you what happens to every app's DNS requests.
Can my DNS provider see my queries when I use DoH?
With ordinary DoH, the chosen resolver processes the queries. Read its data practices; transport encryption is not a substitute for provider trust.
Does HTTPS on a website prove DNS was encrypted?
No. Website HTTPS and DNS transport are separate connections. A secure webpage connection does not establish how the name was resolved.
Should everyone switch DNS providers?
No. Start with a specific privacy, filtering or reliability requirement. Check whether your current setup already meets it and whether a change would interfere with network services you need.